Built for environments where failure has physical consequences.
Trains, airports, plants, utilities, and public missions share one problem: cyber risk that can stop real operations. CYNAPSE gives each sector its own systems, standards, and reports on one common risk and evidence model.
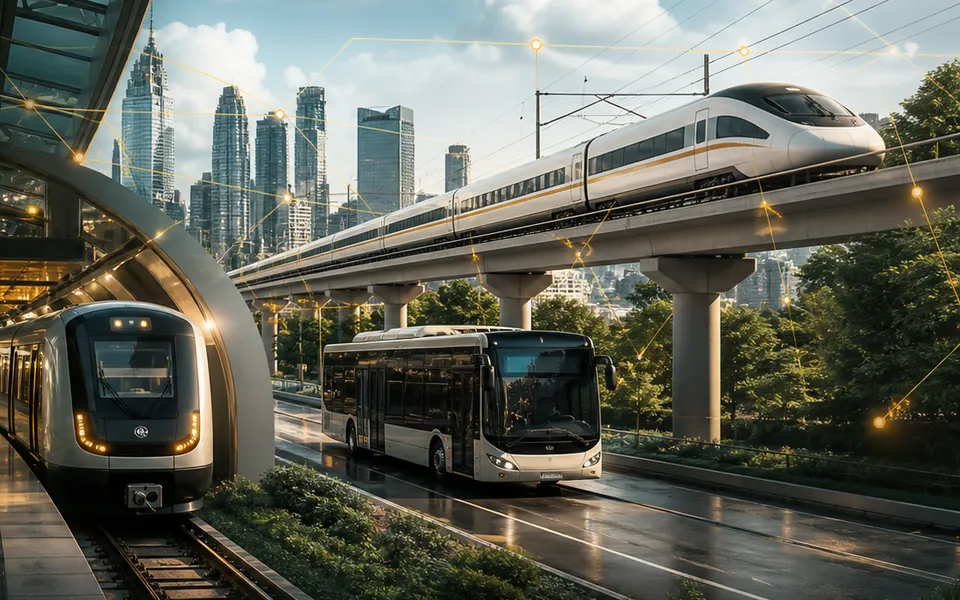
Transportation
Signalling, control centres, rolling stock, and station systems in one evidence trail that satisfies operators, integrators, and assessors.
- Zones and conduits across lines and depots
- EN 50701 and IEC 62443 evidence per subsystem
- Supplier and integrator accountability
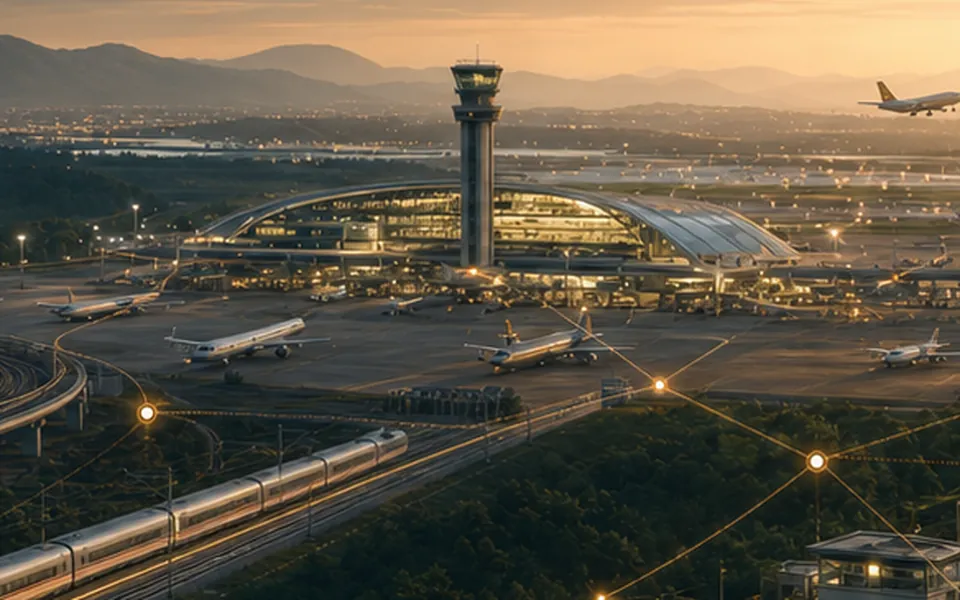
Airports
Passenger, baggage, airside, and building systems mapped as one system of systems, with every supplier connection accounted for.
- Dependency map across terminal and airside
- Vendor remote access under control
- Readiness evidence for regulators and airlines
Industrial OT & ICS
IEC 62443 zones, conduits, and security levels for real plants, with treatment that respects safety, uptime, and patch windows.
- SL-T versus SL-A gaps per zone
- OT-safe exposure discovery
- Validation procedures from applied hardening
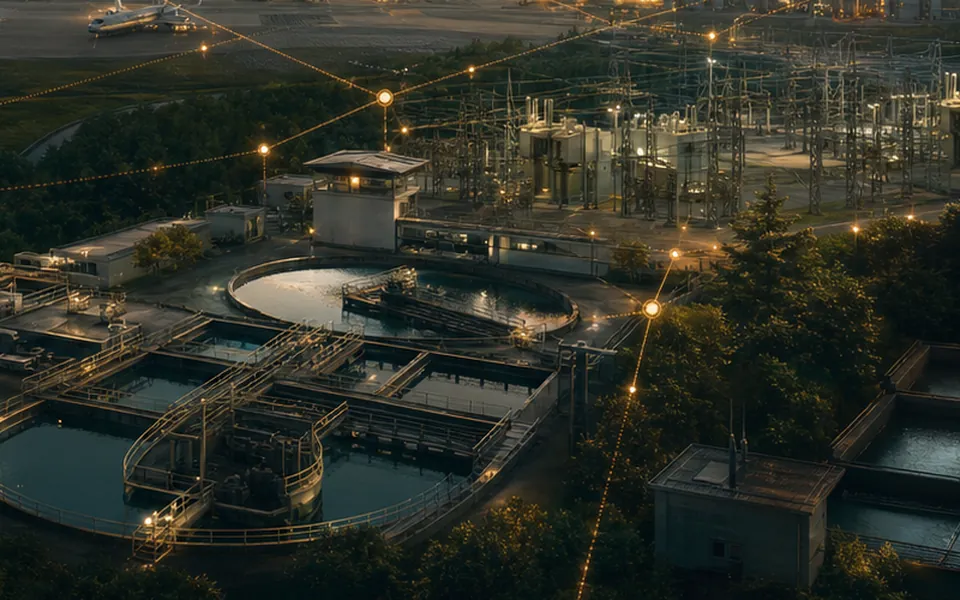
Energy & Water
From substations and pumping stations to the control centre: consequence-led risk for services the public cannot do without.
- Remote site and telemetry exposure
- Consequence scenarios: loss of control, supply, safety
- Evidence for regulators and boards
Public & Defense
Controlled, explainable governance for mission systems and their suppliers, ending in a security case leaders can sign.
- Mission dependency mapping
- Supplier and inherited-control assurance
- Formal security cases with approvals
One risk and evidence model underneath.
Sector pages differ in systems and standards. The way CYNAPSE turns them into decisions stays the same, so portfolio owners compare like with like.
Model
Facilities, systems, assets, zones, conduits, and flows as they really are.
Prioritize
Risk and exposure ranked by operational consequence, not severity alone.
Validate
Controls tested against the hardening actually applied, with evidence.
Decide
Security cases and reports leadership, auditors, and engineers can sign.
Not sure where your programme fits?
Tell us your sector and systems, and we will show the workflow and reports that match.